GDPR-compliant email marketing for venues: a practical checklist
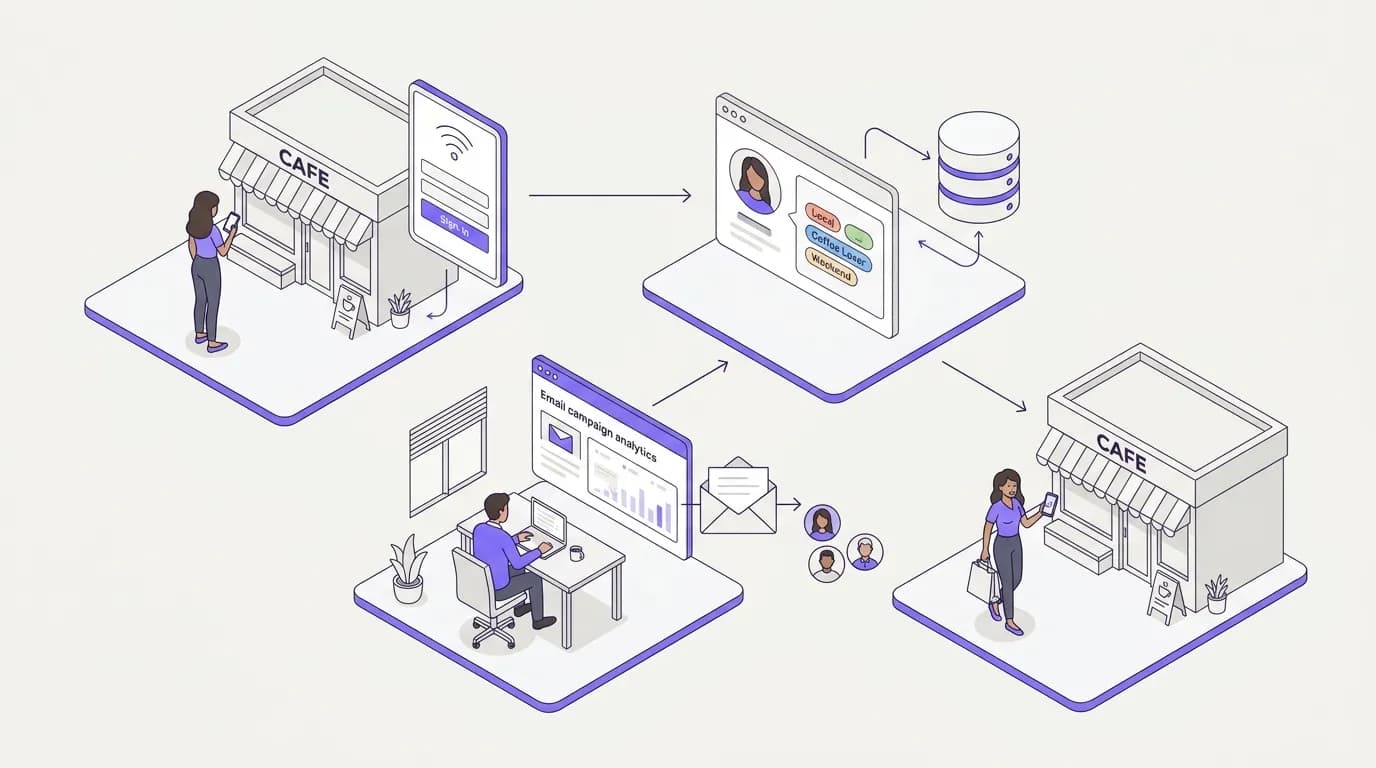
This practical checklist guides venue marketers through the essentials of GDPR-compliant email marketing. It covers conscious-choice opt-ins, data storage, automated opt-outs, and how Purple Engage builds a compliant first-party data list directly from guest WiFi logins.
Video overview
Listen to this guide
Read the transcript
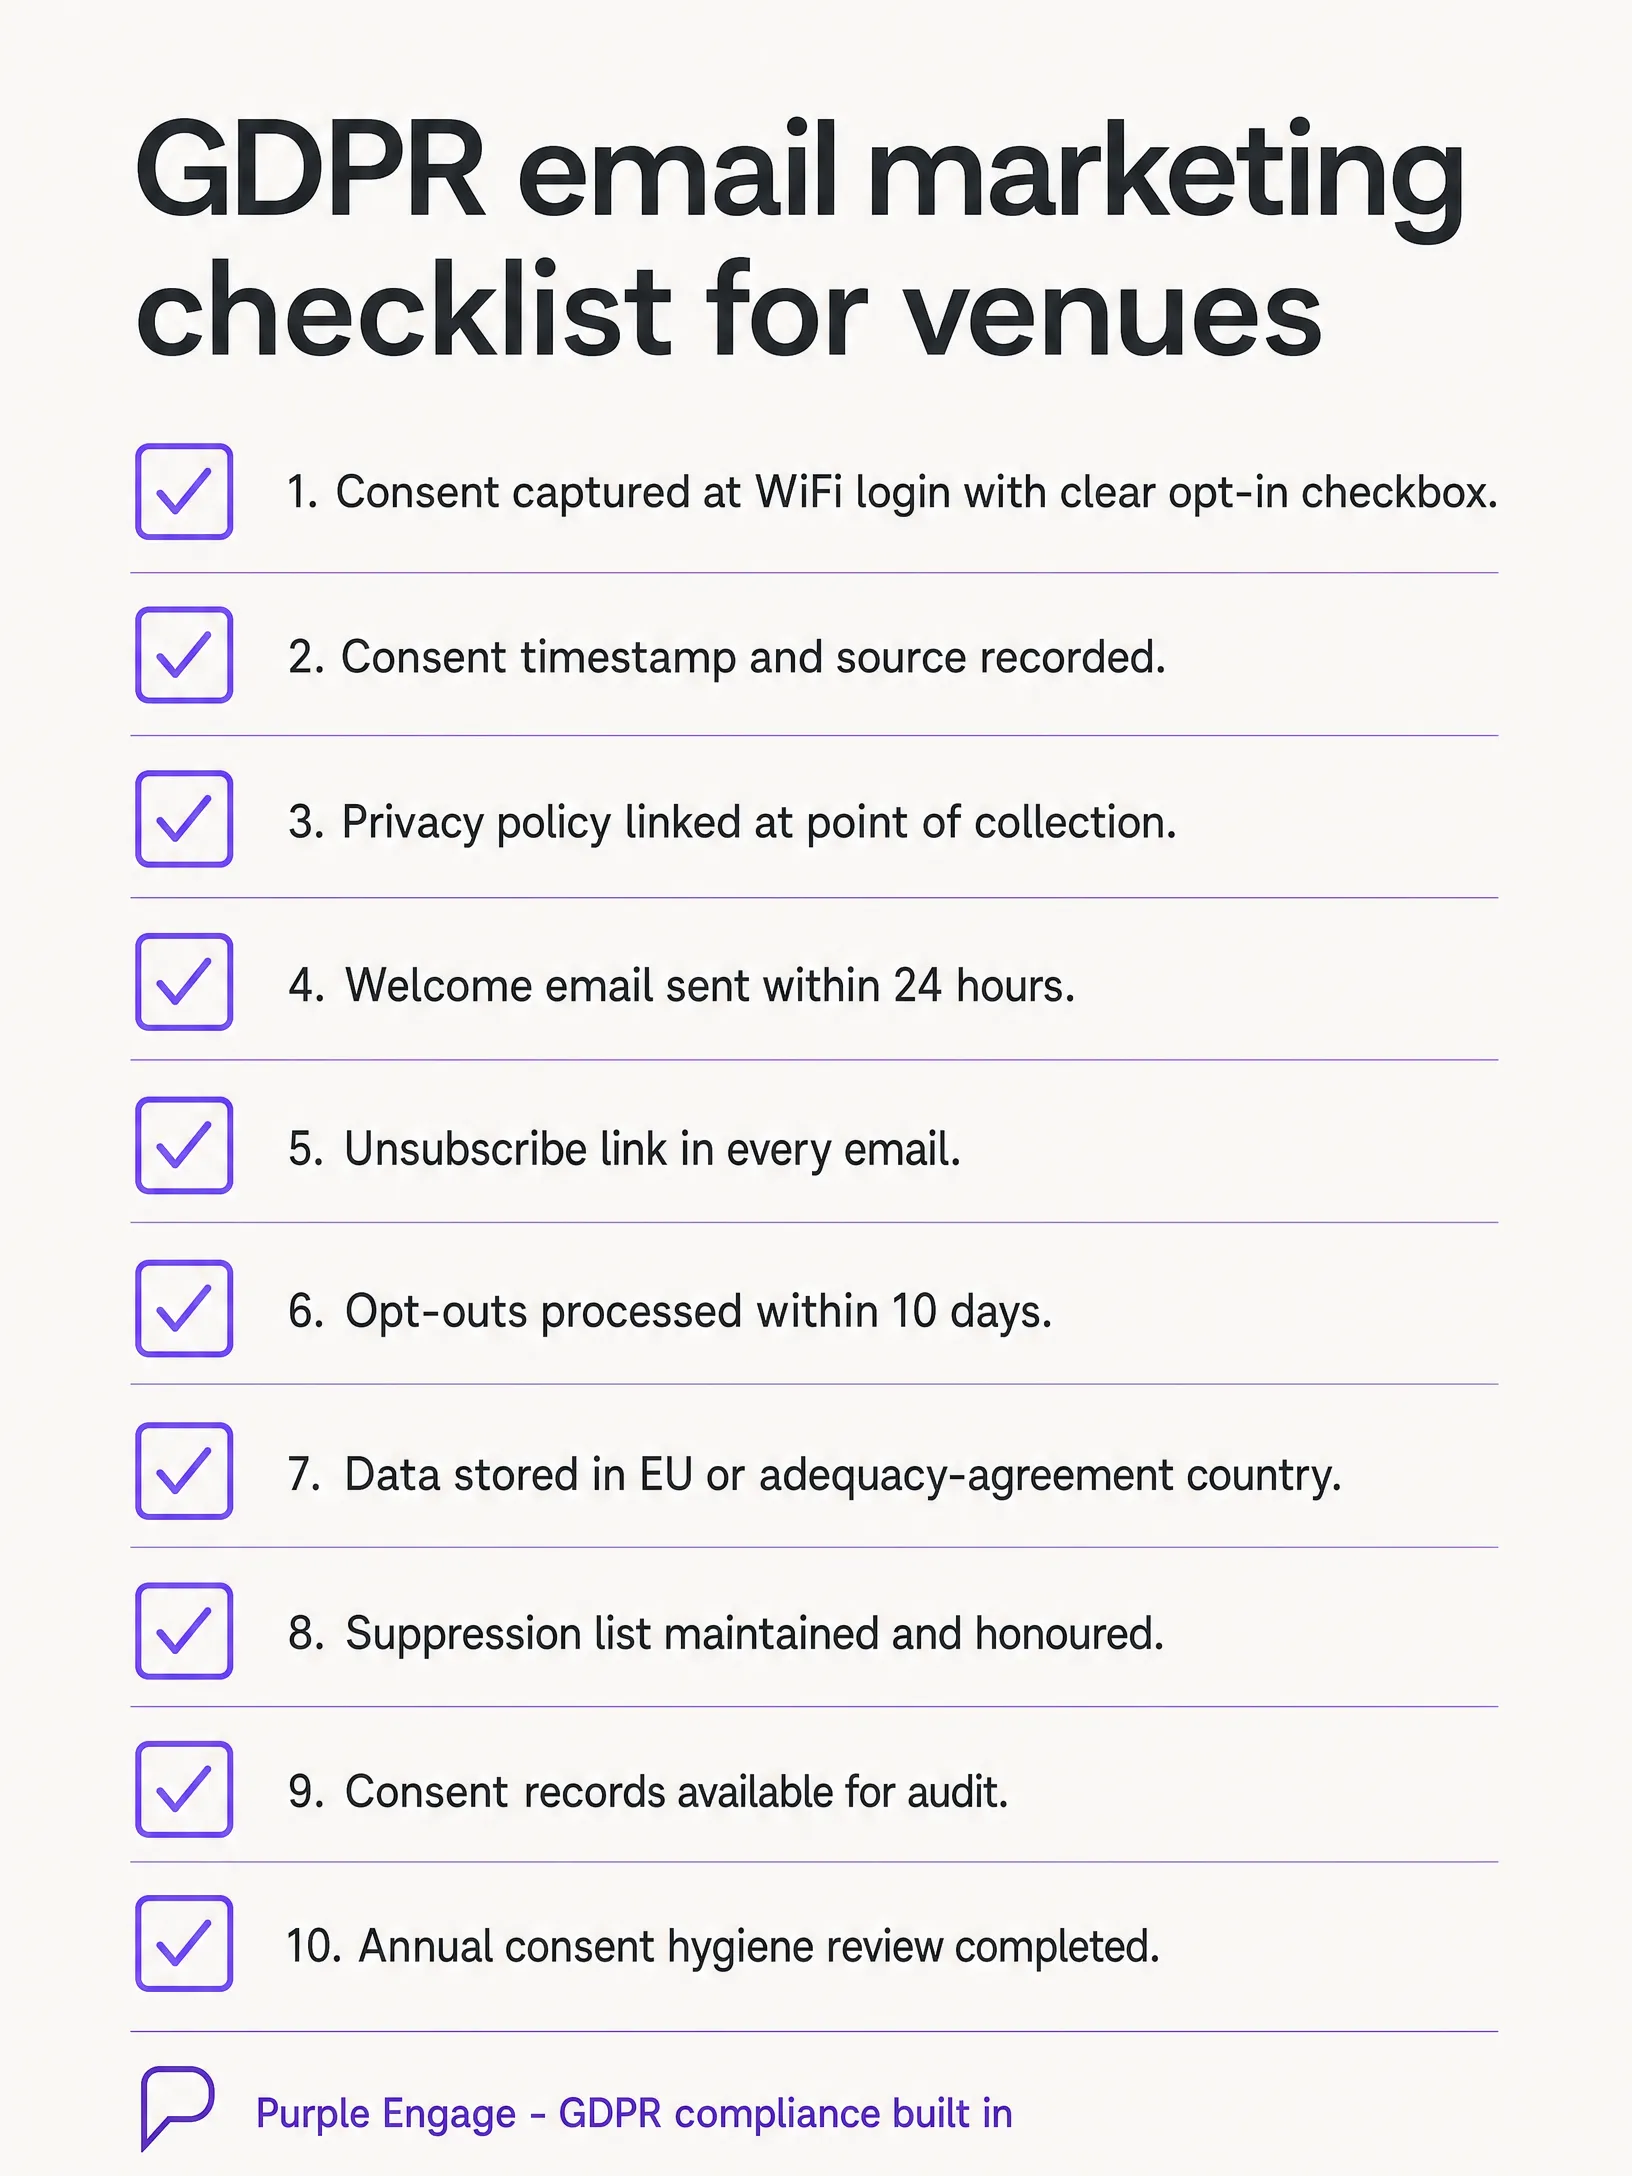
Welcome to the Purple Engage marketing series. I'm your host, and today we're talking about something that every venue marketer needs to get right: GDPR-compliant email marketing. Whether you run a restaurant group, a hotel, a bar, or a retail chain, this episode gives you a plain-English checklist you can act on today. Let's start with why this matters. --- Why it matters --- Here's the uncomfortable truth. Most venues are sitting on a goldmine of foot traffic and doing almost nothing with it. Guests walk in, spend money, and walk out. No follow-up. No reason to come back. No relationship. Email marketing fixes that. A well-timed email to a guest who visited three weeks ago can bring them back through the door. A birthday offer sent to a diner who gave you their details at login can generate a booking that would never have happened otherwise. Venues using Purple Engage see open rates above 40% on first-party data lists, compared to industry averages of around 21% for purchased or scraped lists. That difference is consent. When someone actively chooses to hear from you, they read what you send. But here's the catch. Under GDPR - the General Data Protection Regulation - you cannot just collect email addresses and start sending. You need explicit, informed, freely given consent. And you need to be able to prove it. Get this wrong and you are looking at fines of up to 20 million euros, or 4% of global annual turnover, whichever is higher. The ICO - that's the Information Commissioner's Office in the UK - issued over 7 million pounds in fines in 2023 alone for marketing consent failures. The good news? If you capture consent correctly at the point of WiFi login, you are already most of the way there. That is exactly what Purple Engage is built to do. --- The approach --- Let me walk you through the five pillars of GDPR-compliant email marketing for venues. Pillar one: consent capture. GDPR requires that consent is freely given, specific, informed, and unambiguous. In plain English, that means your guest needs to actively tick a box - not a pre-ticked box, not a buried clause in your terms - to say yes, I want to receive marketing emails from you. When a guest connects to your venue WiFi through Purple Engage, they see a captive portal - a splash page that loads before they get online. That page includes a clearly labelled opt-in checkbox. The wording matters. It should say something like: "I'd like to receive offers and news from The Crown Hotel. You can unsubscribe at any time." Short, clear, honest. No legalese. The checkbox must be unticked by default. Ticking it is the guest's active choice. That is what makes it a conscious-choice opt-in - and that is the phrase we use at Purple because it captures exactly what GDPR demands. Pillar two: consent records. Capturing consent is not enough. You need to be able to prove it. Under GDPR Article 7, if you are challenged by a guest or investigated by a regulator, you must demonstrate that consent was given. That means recording the timestamp of when consent was given, the source - in this case, the WiFi login portal - the exact wording the guest agreed to, and the version of your privacy policy that was in force at the time. Purple Engage records all of this automatically. Every opt-in is timestamped, tagged to the venue, and stored against the guest profile. If the ICO ever comes knocking, you can pull the consent record in seconds. Pillar three: data storage and security. Under GDPR, personal data - including email addresses - must be stored securely and, for UK and EU organisations, either within the UK or EU, or in a country that has an adequacy agreement with the UK or EU. Purple's infrastructure is ISO 27001 certified and GDPR-compliant. Data is stored in EU-based data centres. You do not need to worry about cross-border transfer issues when you use Purple Engage. You also need to ensure that only authorised staff can access your guest data. Purple Engage uses role-based access controls, so your marketing manager can run campaigns without being able to export the full database. Pillar four: opt-out mechanics. Every marketing email you send must include a clear, working unsubscribe link. Under GDPR, an opt-out request must be honoured promptly - the ICO guidance says within a reasonable time, and best practice is within 10 working days. In practice, Purple Engage processes unsubscribes automatically. When a guest clicks unsubscribe, they are added to your suppression list immediately. They will not receive another email from you. You do not need to manually manage this. The suppression list is critical. It is not enough to delete someone from your active list. You need to keep a record that they opted out, so that if their email address is re-added later - say, through a data import - the system knows not to email them. Purple Engage maintains this suppression list automatically. Pillar five: data retention and hygiene. GDPR's storage limitation principle says you should not keep personal data for longer than necessary. For email marketing, that means you need a data retention policy. A sensible approach for most venues is to review consent every 24 months. If a guest has not engaged with any of your emails in two years and has not visited your venue, their consent may no longer be meaningful. Send a re-consent email. If they do not respond, remove them from your active list. This is not just a compliance exercise. It is also good marketing. A clean, engaged list will always outperform a large, stale one. Deliverability improves. Open rates improve. Revenue per send improves. --- Practical steps and pitfalls --- Now let me give you the practical checklist. These are the ten things you need to have in place before you send your first campaign. One. Consent captured at WiFi login with an unticked opt-in checkbox and clear wording. Two. Consent timestamp and source recorded automatically against each guest profile. Three. Privacy policy linked at the point of consent - the splash page must include a link to your full privacy policy. Four. Welcome email sent within 24 hours of opt-in. This is your highest-performing email. Open rates on welcome emails average 50% or above. Do not waste it. Five. Unsubscribe link in every email, clearly visible - not buried in small print at the bottom. Six. Opt-outs processed within 10 working days. With Purple Engage, this is automatic. Seven. Data stored in the UK, EU, or an adequacy-agreement country. Check with your email platform if you are not using Purple Engage. Eight. Suppression list maintained and honoured. Never import a list without checking it against your suppression list first. Nine. Consent records available for audit. You should be able to export a consent report at any time. Ten. Annual consent hygiene review. Set a calendar reminder. Review your list once a year. Re-consent anyone who has been inactive for 18 months or more. Now, the pitfalls. The most common mistake I see venues make is importing a list from a previous system without checking consent provenance. Just because someone gave their email address to your old loyalty programme does not mean they consented to receive emails from your new CRM. If you cannot prove the consent, do not email them. The second pitfall is vague consent wording. "I agree to the terms and conditions" does not cover marketing emails. Consent must be specific. If you want to send promotional emails, your opt-in checkbox must say so explicitly. The third pitfall is ignoring soft opt-outs. Some guests will not click unsubscribe - they will just stop opening your emails. After six months of zero engagement, treat them as effectively opted out. Stop emailing them, or send a re-engagement email before you do. --- Quick Q&A --- Let me answer a few questions I hear regularly from venue marketers. Question: Can I use legitimate interests instead of consent for email marketing? Answer: In theory, yes - GDPR allows legitimate interests as a lawful basis. But the ICO's guidance for direct marketing is clear: consent is the preferred basis, and legitimate interests is harder to defend for promotional emails to consumers. Stick with consent. It is cleaner, more defensible, and actually produces better results because your list is more engaged. Question: Do I need a separate opt-in for SMS marketing? Answer: Yes. Consent for email does not cover SMS. If you want to send text messages, you need a separate opt-in for that channel. Purple Engage supports multi-channel consent capture - you can add an SMS opt-in checkbox alongside the email opt-in on your splash page. Question: What happens if a guest asks me to delete all their data? Answer: That is a Subject Access Request or a Right to Erasure request under GDPR Articles 15 and 17. You have one month to respond. Purple Engage allows you to delete a guest profile from the platform. Note that you are required to keep some records for legal or financial reasons - for example, transaction records - but marketing data should be deleted promptly. --- Summary and next steps --- Let me bring this together. GDPR-compliant email marketing for venues is not complicated, but it does require discipline. The foundation is consent - explicit, timestamped, and provable. Build on that with clean data storage, automatic opt-out processing, and regular list hygiene, and you have a programme that is both legally sound and commercially effective. The venues that get this right are building something that Mailchimp, Klaviyo, and HubSpot cannot give them: a list that builds itself from real guests who have made a conscious choice to hear from you. That is first-party data. And in a world where third-party cookies are disappearing and paid media costs are rising, first-party data is the most valuable marketing asset you can own. Purple Engage captures conscious-choice opt-ins at WiFi login, timestamps every consent record, and handles unsubscribes automatically. GDPR compliance is built in - not bolted on. Your next steps are simple. First, audit your current consent capture process. Is your opt-in checkbox unticked by default? Is the wording specific to marketing emails? Second, check your data storage. Where is your guest data held, and is it GDPR-compliant? Third, test your unsubscribe flow. Click the unsubscribe link in one of your own emails and check that it works and that the opt-out is processed within 10 days. If you want to see how Purple Engage handles all of this automatically, visit purple.ai and take a look at the Engage product. You can also find our full email segmentation guide in the marketing guides section of the site. Thanks for listening. I'll see you in the next episode.
Why this matters for your venue
Most venues are sitting on a goldmine of customer footfall but are doing almost nothing with it. Guests arrive, spend money, and leave. You have no follow-up. There is no reason for them to return. No relationship.
Email marketing solves this problem. A well-timed email to a guest who visited three weeks ago can bring them back through your doors. A birthday offer sent to a diner who provided their details at login can generate a booking that would otherwise never have happened. Venues using Purple Engage see open rates of over 40% on first-party data lists, compared to an industry average of around 21% for purchased or scraped lists. The reason for this difference is consent. When someone actively chooses to hear from you, they read the emails you send.
But here is the catch. Under GDPR, you cannot simply collect email addresses and start sending. You need clear, informed, and freely given consent. And you must be able to prove it. Getting this wrong can cost you fines of up to €20 million or 4% of global annual turnover, whichever is higher.
The good news is that if you collect consent correctly during Guest WiFi login, you are already more than halfway there. Purple Engage is built to do exactly this.
The method
Let's go through the five pillars of GDPR-compliant email marketing for venues.
Pillar 1: Consent capture
GDPR requires consent to be freely given, specific, informed, and unambiguous. In simple terms, this means your guest must actively tick a box - not a pre-ticked box, and not a clause hidden in your terms and conditions - to say yes, I want to receive marketing emails from you.
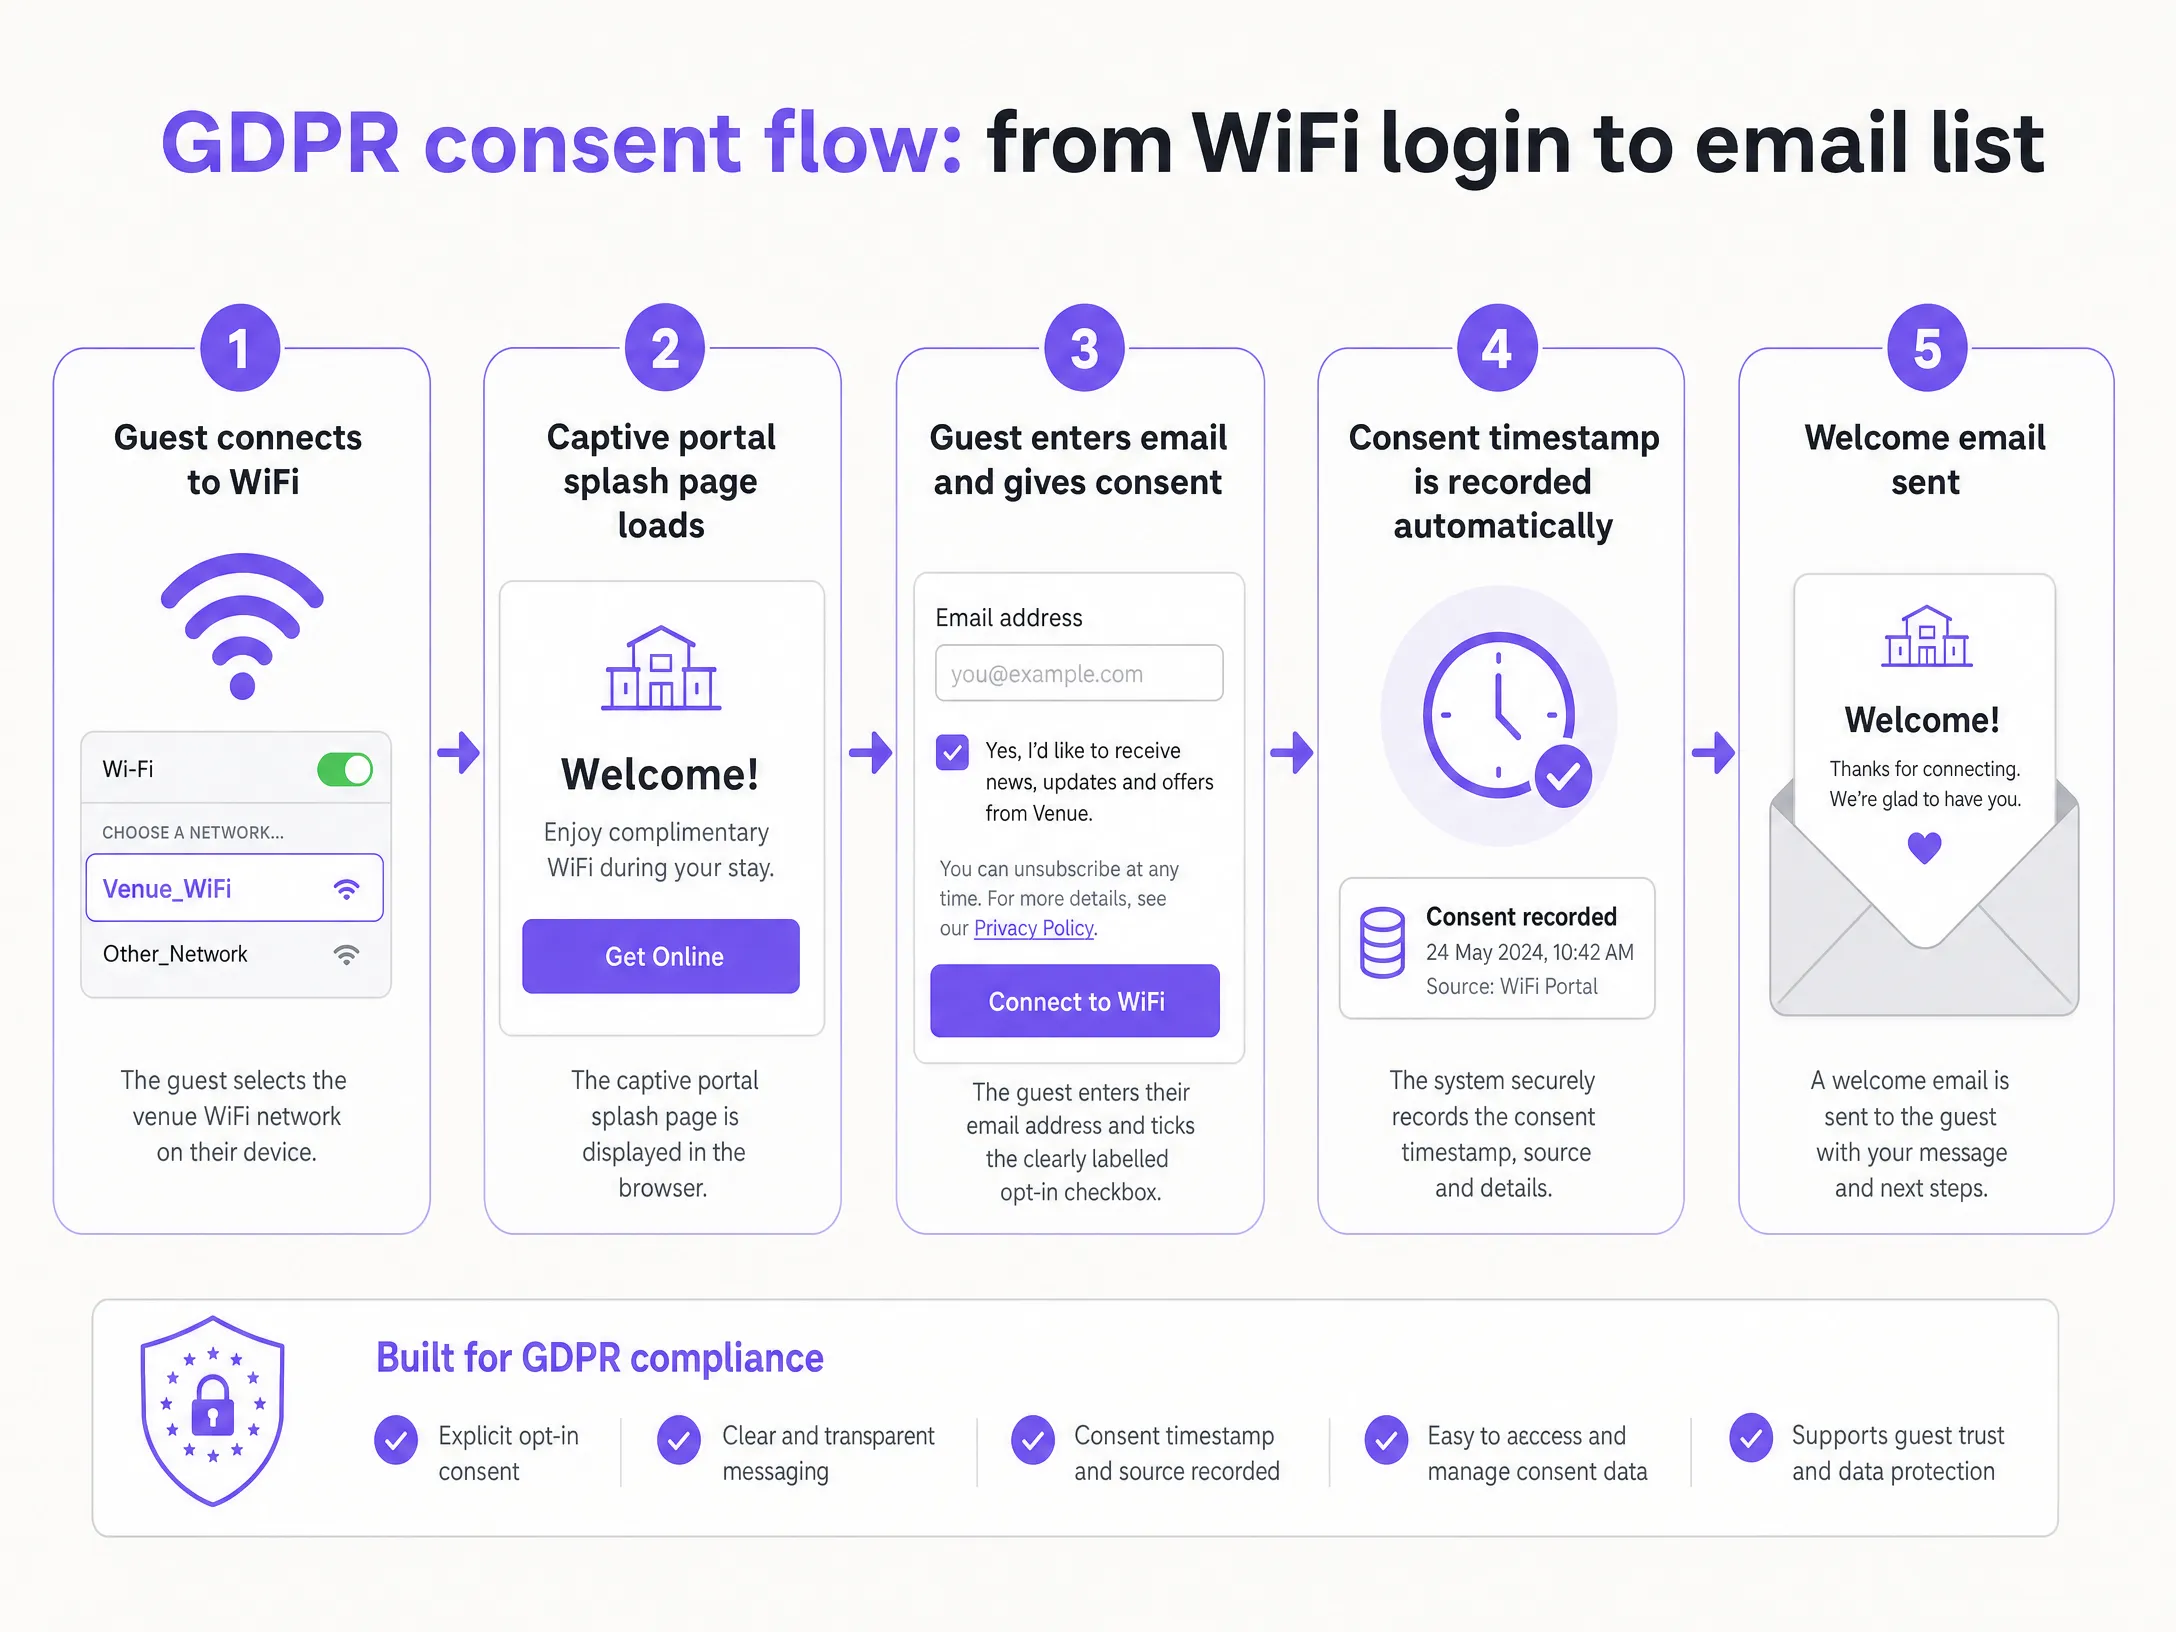
When a guest connects to your venue's WiFi via Purple Engage, they see a Captive Portal - a splash page that loads before they go online. On that page is a clearly labelled opt-in checkbox. The language is important. It should be something like: "I would like to receive offers and news from The Crown Hotel. You can unsubscribe at any time." Short, clear, honest. No complex legalese.
The checkbox must be unticked by default. Ticking it is the guest's active choice. This is what makes it a conscious-choice opt-in - and this is the phrase we use at Purple because it captures exactly what GDPR demands.
Pillar 2: Consent records
Collecting consent is not enough. You must be able to prove it. Under GDPR Article 7, if you are challenged by a guest or investigated by a regulatory body, you must prove that consent was given. This means recording the timestamp of when consent was given, the source - in this case, the WiFi login portal - the exact wording the guest agreed to, and which version of your privacy policy was active at the time.
Purple Engage records all of this automatically. Every opt-in is timestamped, tagged to the venue, and stored in the guest profile. If the ICO ever investigates, you can pull up the consent record in seconds.
Pillar 3: Data storage and security
Under GDPR, personal data - including email addresses - must be stored securely and, for UK and EU organisations, within the UK or EU, or in a country that has an adequacy agreement with the UK or EU. Purple's infrastructure is ISO 27001 certified and GDPR-compliant. Data is stored in EU-based data centres. You do not have to worry about cross-border data transfer issues when you use Purple Engage.
You also need to ensure that only authorised staff can access your guest data. Purple Engage uses role-based access control, so your marketing manager can run campaigns without exporting the entire database.
Pillar 4: Opt-out mechanics
Every marketing email you send must contain a clear, working unsubscribe link. Under GDPR, an opt-out request must be actioned quickly - within a reasonable timeframe according to ICO guidelines, with best practice being within 10 working days. In reality, Purple Engage processes unsubscribes automatically. When a guest clicks unsubscribe, they are immediately added to your suppression list. They will not receive another email from you. You do not have to manage this manually.
The suppression list is crucial. Simply deleting someone from your active list is not enough. You must keep a record that they have opted out, so that if their email address is added again later - say, via a data import - the system knows not to email them. Purple Engage maintains this suppression list automatically.
Pillar 5: Data retention and hygiene
GDPR's storage limitation principle states that you should not keep personal data for longer than you need it. For email marketing, this means you need a data retention policy. A sensible approach for most venues is to review consent every 24 months. If a guest has not interacted with any of your emails and has not visited your venue in two years, their consent may no longer be meaningful. Send a re-consent email. If they do not respond, remove them from your active list.
This is not just a compliance exercise. It is also good marketing. A clean, active list will always outperform a large but disengaged one. Deliverability improves. Open rates go up. Revenue per email increases.
How to do this with your Guest WiFi
Venues that get this right are building something that Mailchimp, Klaviyo, and HubSpot cannot give them: a list that builds itself from real guests who have made a conscious choice to hear from you. This is first-party data. And in a world where third-party cookies are disappearing and paid media costs are rising, first-party data is the most valuable marketing asset you own.
Purple Engage captures conscious-choice opt-ins during WiFi login, timestamps every consent record, and handles unsubscribes automatically. GDPR compliance is built-in - not bolted on.
To learn more about how to segment this data, read our Email segmentation for venues: a practical guide.
What to send and when to send it
Once you have a consented list, you need to send emails that drive revenue.
Welcome emails Send this within 24 hours of opt-in. This is your best-performing email. Welcome emails have an average open rate of 50% or higher. Include a clear offer to encourage a repeat visit.
Birthday offers If you collect date of birth at login, set up an automated birthday email 14 days before the date. This drives high-value group bookings.
Re-engagement campaigns Send an offer to guests who have not visited in 90 days. This turns one-time visitors into loyal regulars.
Measuring what works
Do not just measure opens and clicks. Measure repeat visits and revenue.
Because Purple Engage tracks WiFi logins, you can see when a guest returns to your venue after receiving an email. This is true closed-loop attribution. You will know exactly how much revenue your email marketing is generating.
Where to start
Your next steps are simple.
- Audit your current consent capture process. Is your opt-in checkbox unticked by default? Is the wording specific to marketing emails?
- Check your data storage. Where is your guest data being held, and is it GDPR-compliant?
- Test your unsubscribe flow. Click the unsubscribe link in one of your own emails and check that it works and that the opt-out is processed within 10 days.
Listen to our 10-minute briefing on this topic below.